GitLab BlogGitHub
Uncover the business logic vulnerabilities SAST scanners miss
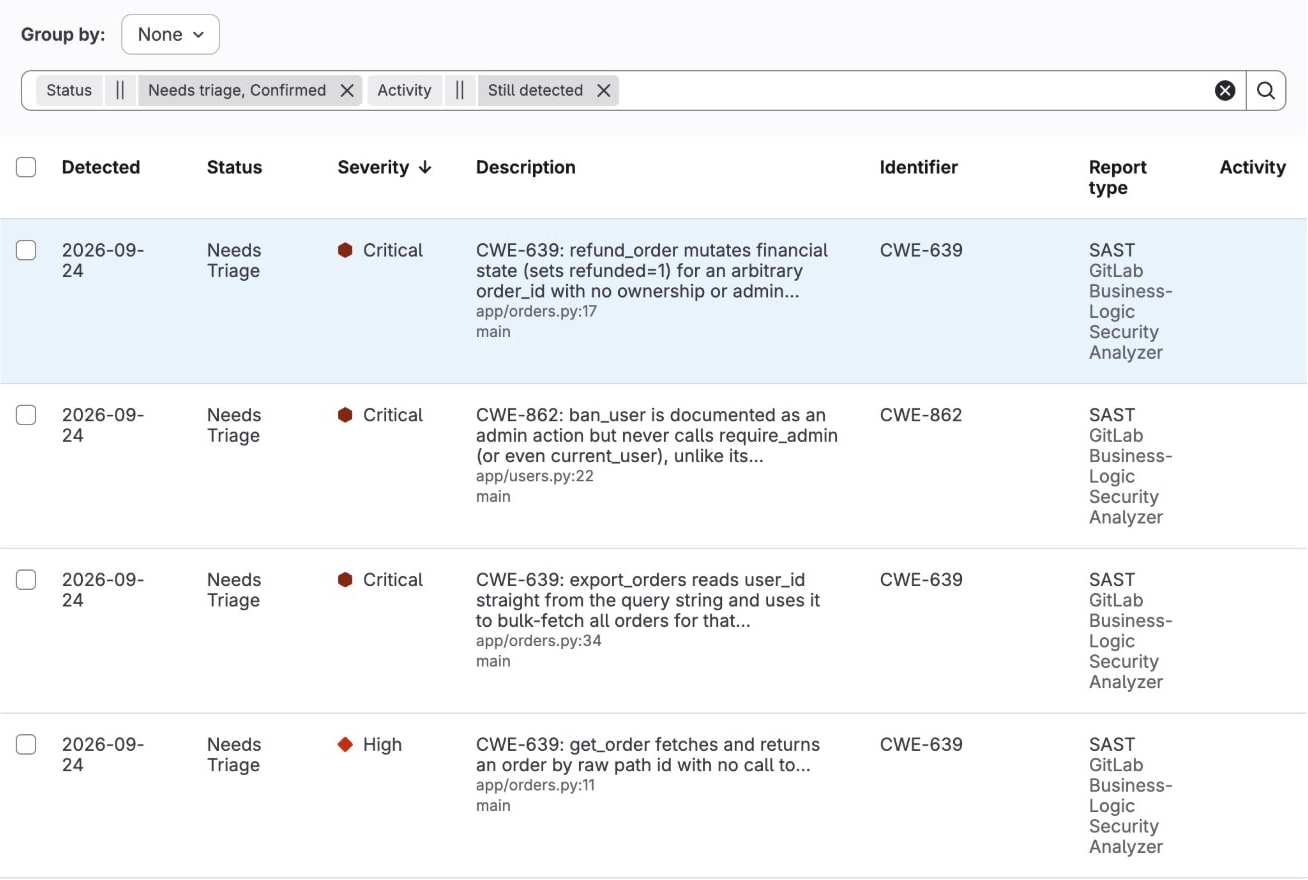
Broken object-level authorization ranks first on the OWASP API Security Top 10 , and OWASP says that traditional static application security testing (SAST) tools struggle to find access control…
Read at GitLab Blog ↗More from GitLab Blog on Accept All
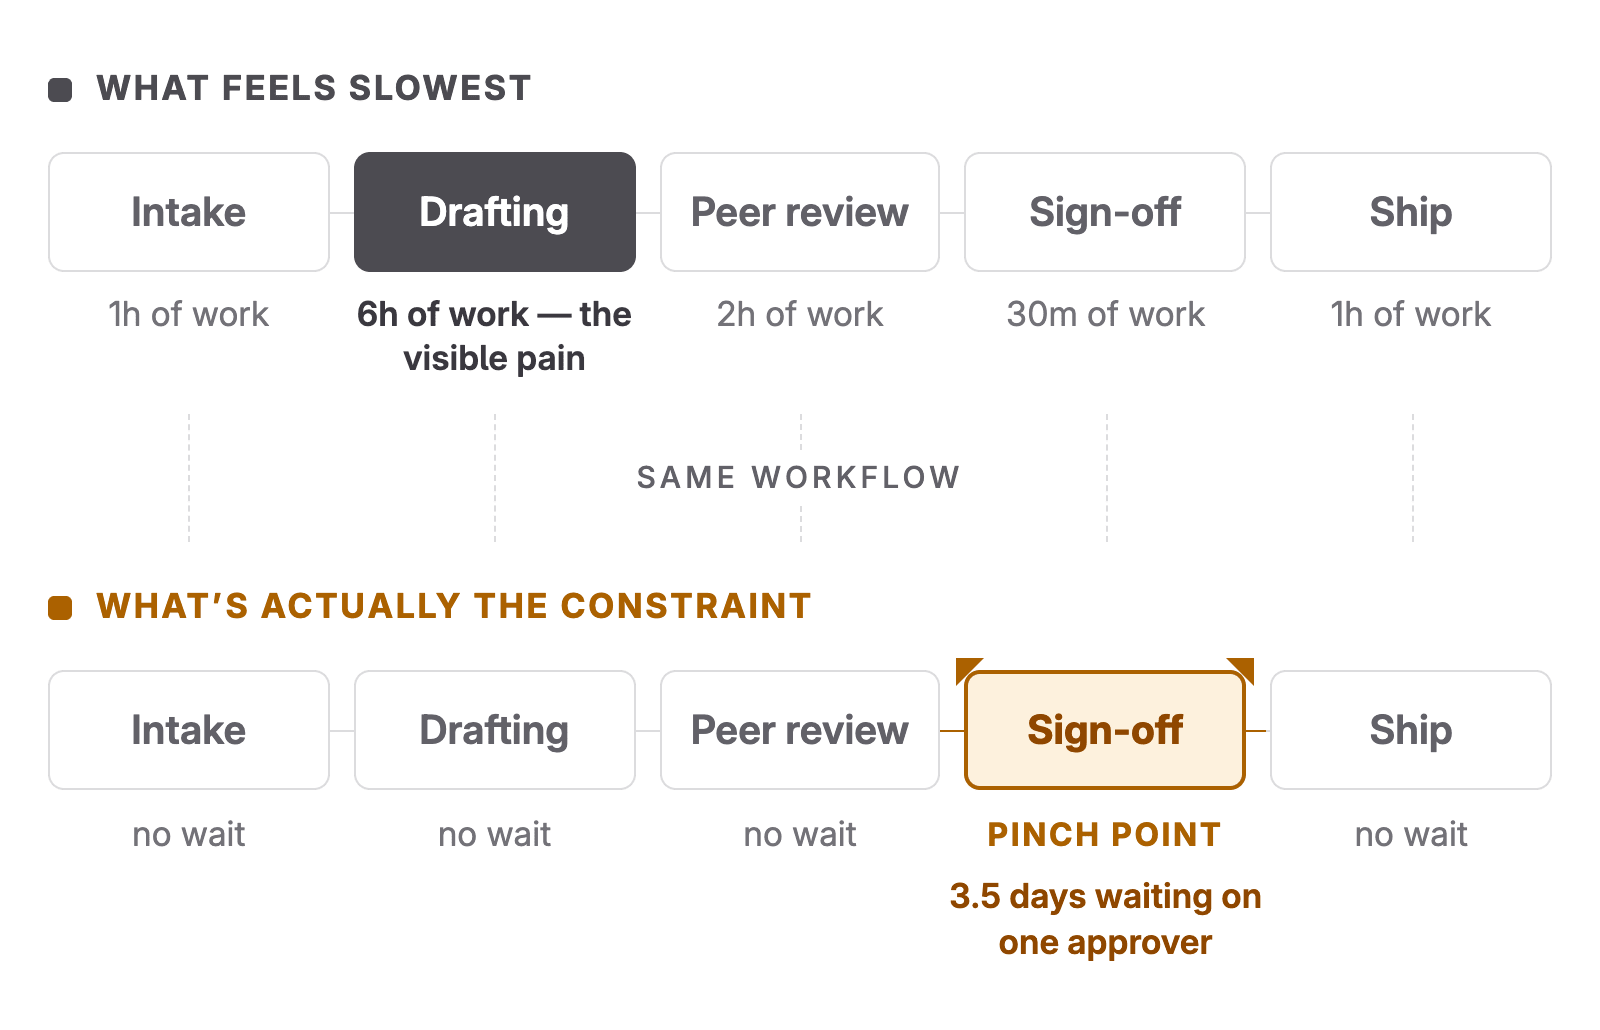
GitHubRedesign how your team ships software with AI agents GitLab Blog
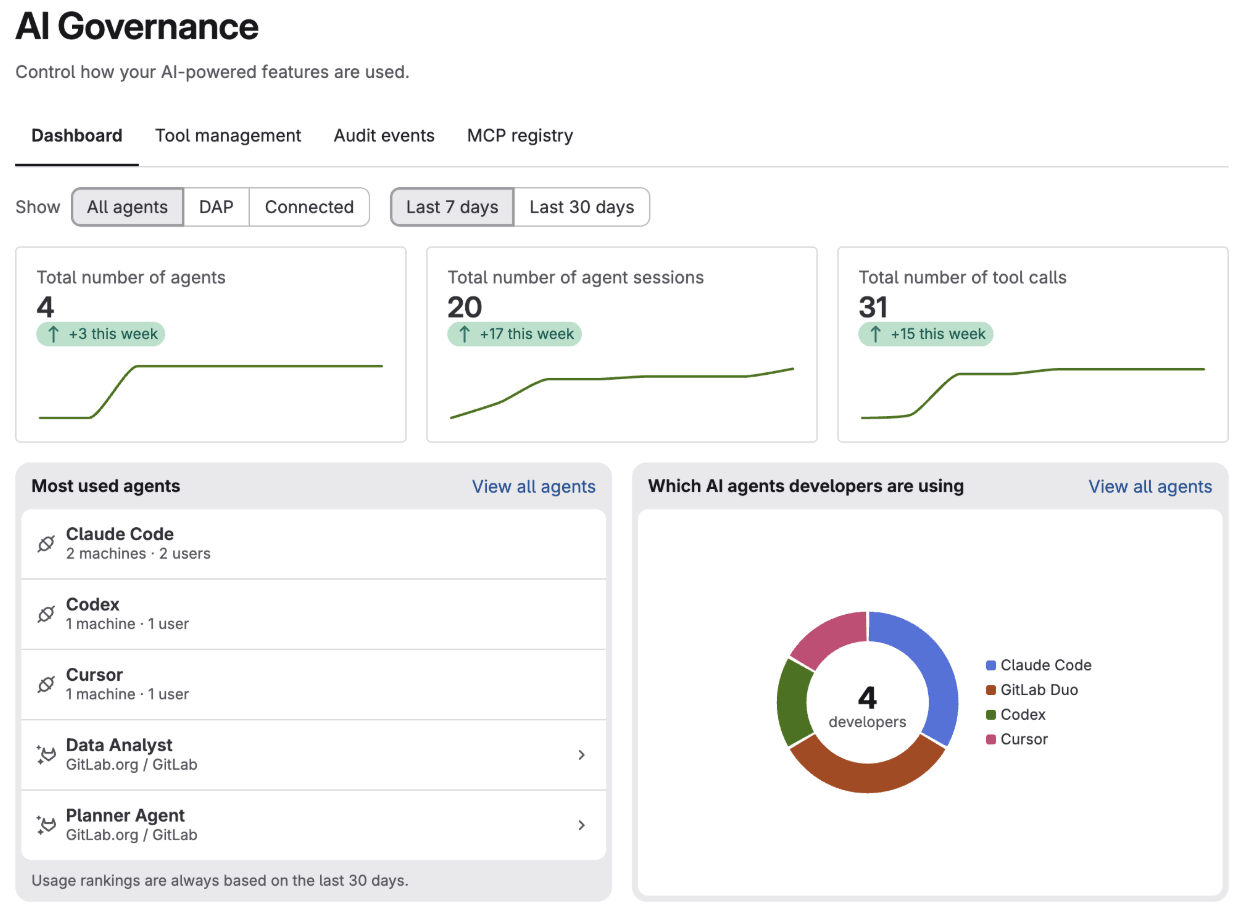
GitHubAI Governance: One view of agent activity GitLab Blog
GitHubThree developer tasks worth handing to an agent GitLab Blog
GitHubBuilding AI security in the open GitLab Blog
GitHubGitLab Secrets Manager: Govern secrets like your code GitLab Blog